FIVE KEYS. ONE BREACH.
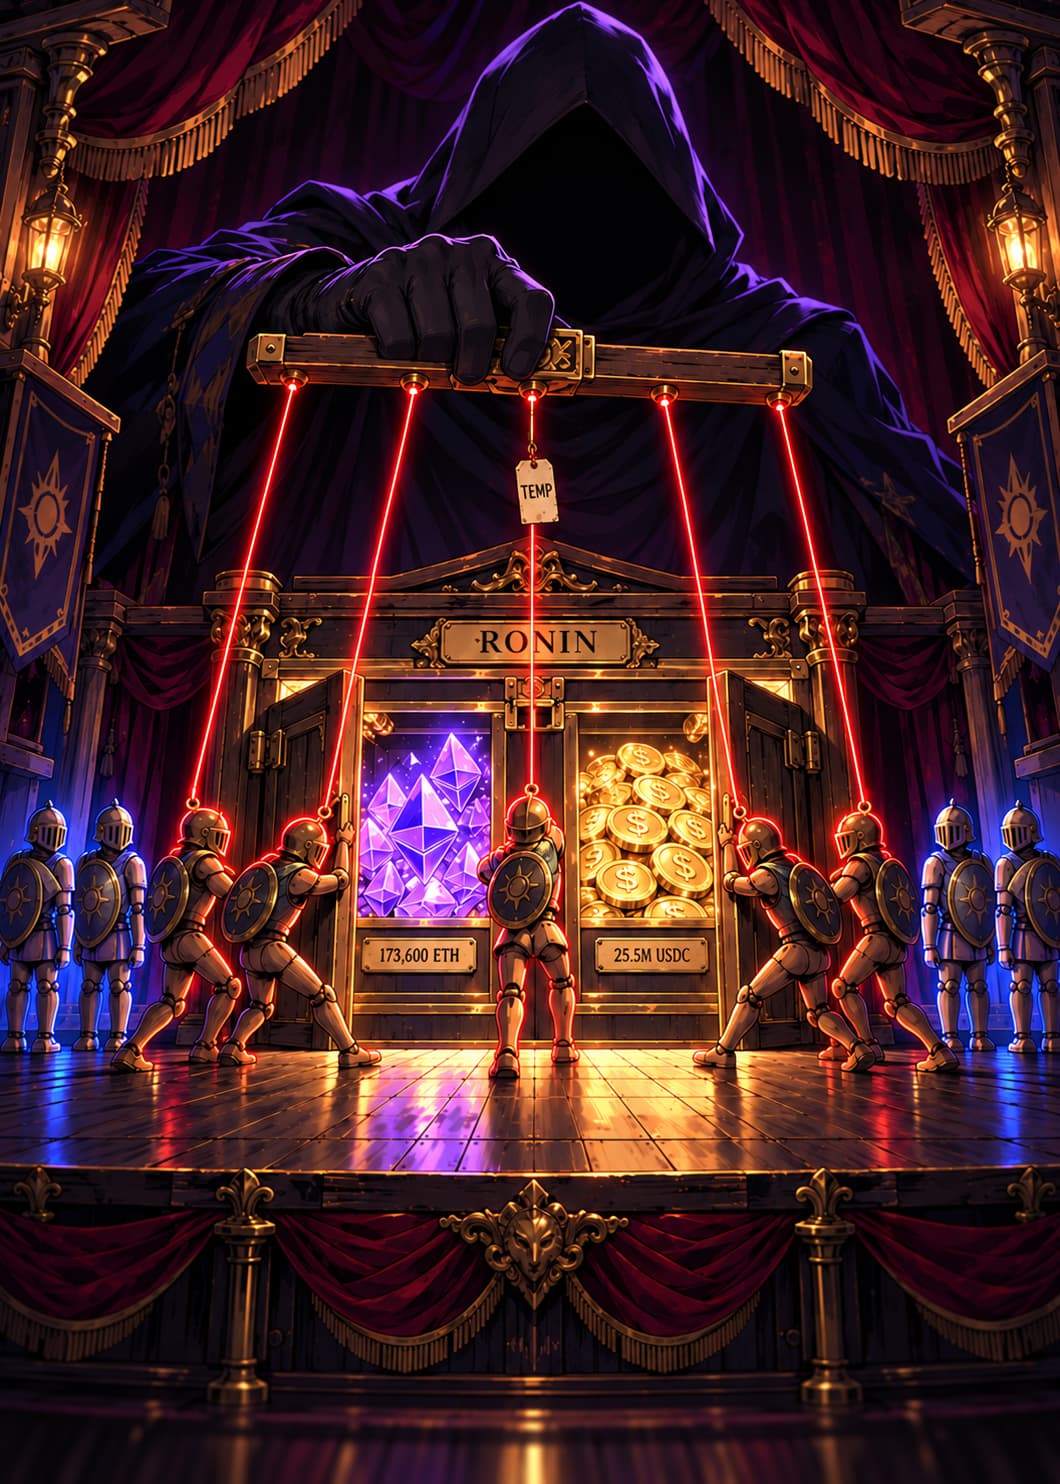
Ronin supported the Axie Infinity game and connected its network with Ethereum through a bridge. On 23 March 2022, attackers used two fraudulent withdrawals to steal 173,600 ETH and 25.5 million USDC from that bridge.
Withdrawals required approval from five of nine validators. The attackers compromised four Sky Mavis validators, then used access to the Axie DAO validator to obtain the fifth approval. Enough signing authority had fallen under their control to make the withdrawals pass.
The extra access came from a temporary arrangement introduced in November 2021 to handle heavy demand. Its use ended in December, but the permission was not revoked. A short-term operational exception remained available to the attackers months later.
The theft went undiscovered for six days. A failed attempt to withdraw 5,000 ETH triggered an investigation, and Ronin disclosed the breach on 29 March. The date on this card marks that public disclosure, rather than the earlier attack.
On 14 April 2022, the FBI attributed the theft to Lazarus Group and APT38, actors associated with North Korea. The faceless puppeteer is a metaphor for stolen control, not a portrait of any identified attacker. The guardians turn the signing threshold into a visible story.
Sources & the artist’s interpretation
Sources: BlockSec fund tracing, 31 March 2022 ; Forta incident analysis, 20 April 2022 ; FBI attribution, 14 April 2022 . The theatre, marionettes, strings and treasury are fictional symbols. Decorative emblems are not attacker insignia. FIVE KEYS. ONE BREACH. is an editorial caption, not a historical quotation. The original Ronin incident post is currently unavailable; surviving security research supports the chronology.